Photo by Markus Winkler from Pexels
Cookie banners are everywhere, yet most of them still get consent wrong. In 2026 the enforcement landscape around GDPR cookie consent has tightened considerably, with record fines, new guidance from the European Data Protection Board (EDPB), and browser-level changes that make old-school "accept all" walls legally risky. Whether you are evaluating a new SaaS tool or simply wondering why a site drops 47 trackers before you click anything, this guide breaks down exactly what the rules require right now, and how to protect yourself.
TL;DR
- Valid cookie consent under GDPR must be freely given, specific, informed, and unambiguous, pre-ticked boxes and dark-pattern banners do not count.
- The ePrivacy Directive works alongside GDPR: you need consent before storing or reading any non-essential cookie on a visitor's device.
- Enforcement has escalated in 2025–2026, with data protection authorities across the EU issuing fines specifically for deceptive consent flows.
- Strictly necessary cookies (session IDs, shopping-cart tokens, security cookies) are the only category exempt from consent.
- Tools like the free Terms Doctor extension can flag sites that bury tracking disclosures deep inside their terms of service, so you know what you are agreeing to before you click "Accept."
Why Cookie Consent Still Matters in 2026
The core legal framework has not changed, GDPR Articles 6 and 7 define consent, and the ePrivacy Directive (Article 5(3)) requires it before any non-essential storage on a user's device, but the interpretation has grown stricter. The EDPB's 2024 guidelines on consent design patterns explicitly list "cookie walls" (blocking content until the user accepts all cookies) as potentially invalid unless a genuine, equivalent alternative is offered.
"The General Data Protection Regulation (GDPR) is the most comprehensive data protection legislation that has been passed by any governing body to this point.">, Cookies, the GDPR, and the ePrivacy Directive
For anyone signing up for SaaS tools, marketplaces, or AI-powered apps, this matters because the cookies a service drops often reveal how it handles your data behind the scenes. A site that ignores consent rules on cookies is unlikely to be careful with the personal data it collects through its terms of service, either.
The Six Legal Requirements for Valid Cookie Consent
Under GDPR and the ePrivacy Directive combined, cookie consent must satisfy all six of the following conditions to be legally valid:
- Freely given, The user must have a genuine choice. Consent is not free if refusing cookies means losing access to the service entirely (unless cookies are strictly necessary for the service to function).
- Specific, Consent must be collected per purpose. A single "Accept all" toggle that bundles analytics, advertising, and personalisation into one action does not meet the specificity requirement unless the user can also accept each category individually.
- Informed, Before consenting, the user must know: who is setting the cookies, what each category does, how long the cookies last, and whether data is shared with third parties.
- Unambiguous, Consent requires a clear affirmative action, a click, a toggle, a swipe. Scrolling the page or continuing to browse is not valid consent, despite what some older consent management platforms still claim.
- Revocable, Users must be able to withdraw consent as easily as they gave it. If accepting takes one click, rejecting or withdrawing must take no more than one click, too.
- Documented, The data controller must be able to prove that consent was obtained. This means logging the timestamp, the version of the consent notice shown, and the choices the user made.
Which Cookies Are Exempt?
Not every cookie needs consent. The ePrivacy Directive exempts cookies that are strictly necessary for the service the user explicitly requested. Here is a quick breakdown:
| Cookie type | Example | Consent needed? |
|---|---|---|
| Session / authentication | Login session token | No |
| Shopping cart | Items saved in cart | No |
| Security | CSRF protection token | No |
| Load balancing | Server-routing cookie | No |
| Cookie-consent preference | Stores the user's consent choice | No |
| Analytics (first-party) | Page-view counter | Yes |
| Analytics (third-party) | Google Analytics, Hotjar | Yes |
| Advertising / retargeting | Facebook Pixel, Google Ads | Yes |
| Social-media embeds | YouTube, Twitter widgets | Yes |
| AI personalisation | Recommendation engine tracker | Yes |
Common Dark Patterns to Watch For
Data protection authorities have published increasingly detailed catalogues of consent dark patterns. Here are the ones you will encounter most often in 2026:
- Asymmetric buttons, "Accept all" is a bright green button; "Manage preferences" is a tiny grey link. The CNIL has fined multiple companies specifically for this pattern.
- Pre-ticked categories, The consent dialogue opens with analytics and marketing toggles already switched on. Under GDPR, pre-ticked boxes do not constitute valid consent (confirmed by the CJEU in the Planet49 ruling, Case C-673/17).
- Hidden reject option, There is no "Reject all" on the first layer of the banner. The user must click through to a second screen, then manually untoggle each category.
- Consent wall / cookie wall, The entire page is blocked until the user accepts cookies, with no alternative access path.
- Forced re-consent, The banner reappears on every visit, hoping the user will eventually click "Accept" out of frustration, even though they previously rejected cookies.
- Legitimate interest abuse, Some consent management platforms list advertising cookies under "legitimate interest" rather than consent, bypassing the consent requirement entirely. The EDPB has clarified that tracking for advertising almost never qualifies as a legitimate interest.
How to Audit a Site's Cookie Consent in Five Steps
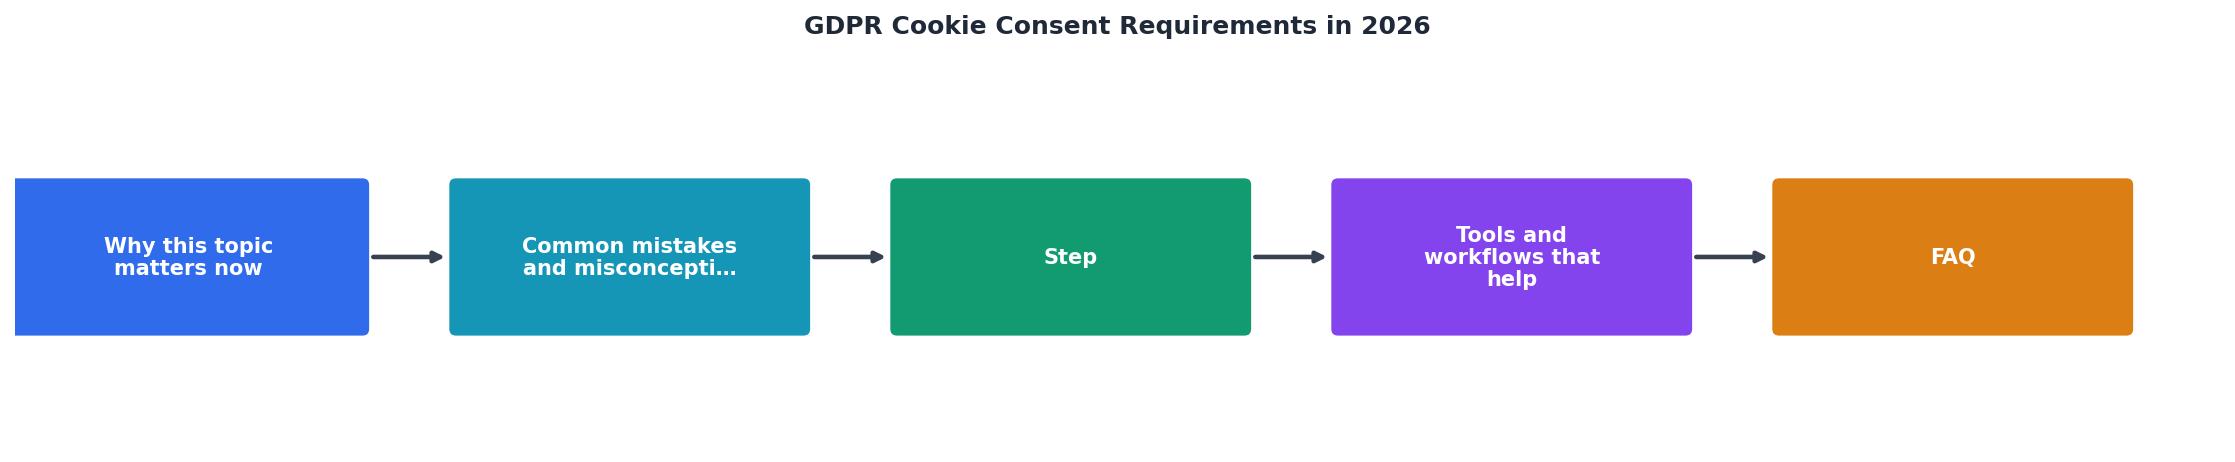
Use this step-by-step process whenever you land on a new service and want to know whether it respects your consent rights:
Cookie Consent Audit Checklist
Your progress is saved automatically in your browser.
What Changed in 2025–2026
Several developments have reshaped the cookie consent landscape since 2024:
- EDPB Guidelines 03/2024 on consent design patterns, These guidelines formalised the requirement for symmetrical accept/reject options and explicitly called out cookie walls.
- Increased cross-border enforcement, The "one-stop-shop" mechanism has been streamlined, meaning complaints about cookie consent filed in one EU country are resolved faster, even when the data controller is based in another.
- Browser-level privacy defaults, Safari and Firefox have blocked third-party cookies by default for years; Chrome's Privacy Sandbox has now fully replaced third-party cookies with the Topics API and Attribution Reporting. This does not eliminate the need for consent, first-party analytics and any server-side tracking still require it, but it changes the technical landscape.
- AI-specific tracking, Many AI-powered tools now use cookies or similar technologies to feed user interaction data back into model training. The EDPB has confirmed that this constitutes a distinct processing purpose requiring its own, separate consent.
FAQ
Frequently Asked Questions
Protect Yourself Without Reading Every Cookie Policy
You should not need a law degree to browse the web safely. The GDPR gives you strong rights around cookie consent, but enforcement still lags behind, and many sites rely on dark patterns to nudge you into accepting everything. The best defence is a combination of awareness and automation.
Install the free Terms Doctor extension for Chrome, Edge, Brave, Opera, or Vivaldi. It finds the terms of service on any site you visit, runs 101 consumer-protection checks, from forced arbitration to auto-renewal traps to AI data-training clauses, and gives you an instant A-F grade. Pair that with the cookie-audit checklist above, and you will catch the vast majority of consent violations before they affect you.
Disclaimer: This article is for informational purposes only and does not constitute legal advice. Automated checks, including those provided by Terms Doctor, are educational tools, consult a qualified legal professional for advice specific to your situation.
Additional Resources
- Cookies, the GDPR, and the ePrivacy Directive - Receive users' consent before you use any cookies except strictly necessary cookies. · Provide accurate and specific information about the data each cookie ...
- Global Cookie Consent Trends 2026: What You Need to ... - Consent must be free, informed, clear, and easy to cancel with one click. It needs to work in 22+ languages. Starting November 2026, Consent ...
- The Practical GDPR Guide for Small and Mid-Sized Websites - Cookie consent in 2026: A practical GDPR guide for small and mid-sized websites. Learn about prior blocking, consent logging, legal conditions, ...